

LAS VEGAS — The HHS Office for Civil Rights finalized modifications to the HIPAA Privacy Rule on Monday, aimed at increasing patients’ access to their own medical records. The rule, initially proposed in 2020, contains a slew of substantive updates to the foundational health data privacy rule that seek to reduce administrative friction and encourage health data sharing.
The final rule slashes the timeframe for providers to respond to patient record requests in half, from 30 calendar days to 15. It also enables providers to share more health information with certain third parties, like social workers, in a play to enhance care coordination. And in line with the Trump administration’s enthusiasm for patient access to digital health tools, patients will also be able to obtain copies of their records via health apps.
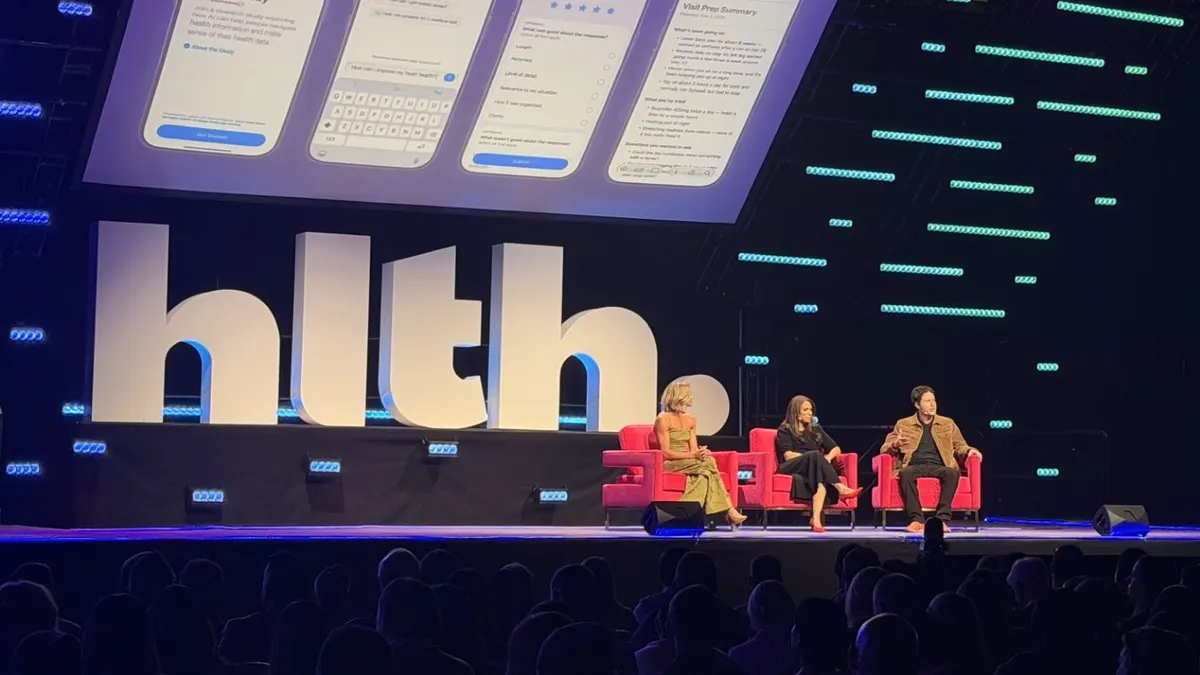
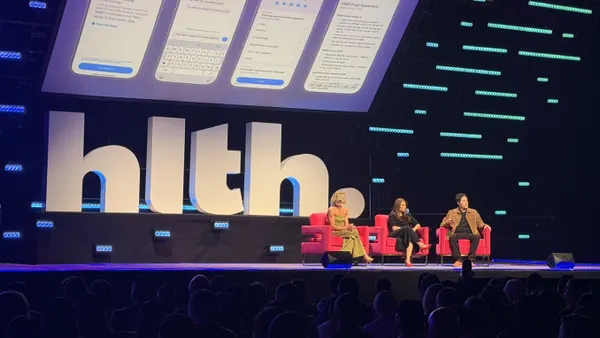
“I know that lots of people have been looking forward to this rule. Some believe that it should have been done much earlier,” OCR Director Paula Stannard said during a session at the HLTH 2026 conference.
“But we are convinced that this will provide individuals with faster access to health information while at the same time facilitating health information interoperability, enhancing care coordination, reducing regulatory burden and protecting the privacy of individual health information as we seek to improve the healthcare system by making information more interoperable.”
The rule will go into effect 60 days after it’s published on the federal register, which is set to happen on Thursday. Healthcare providers, payers and their business associates will be expected to comply around July 10, or roughly six months after the effective date.
The HHS estimates that the rule will result in $784 million in new costs within a year of implementation, but that those upfront costs will be offset by net cost savings of $703 million annually in years two through five.
The department says the majority of the savings will come from eliminating the requirement that healthcare providers obtain a signed acknowledgment of receipt of the notice of privacy practices, which the HHS says currently costs providers significant time and money.
HIPAA revamp targets patient records access, app sharing
When HIPAA was enacted in 1996, the commercial internet was in its infancy and electronic health records were not yet widely adopted. The regulation initially set out to help people transfer health insurance when they switched jobs and to standardize health information, but it later evolved to set standards for privacy and security in the sector.
Since the HIPAA Privacy Rule was tacked onto the law in 2003, it has served as the preeminent federal regulation for safeguarding the privacy and confidentiality of protected health information transmitted by providers, payers and their business associates. It sets strict parameters for how and when healthcare organizations can use or disclose PHI and gives patients the right to request access to their records, mandating that they receive them in a timely manner.
Giving patients access to their medical records has been a priority under President Donald Trump’s OCR, and remains one of the top complaints the agency receives. During his first administration, the OCR launched an enforcement initiative to discipline providers that fail to provide patients timely access to their records, and the agency has cracked down on 55 organizations over the last seven years.
The new rule smooths the road for providers to share health records with patients by adding definitions for “personal health application” and “electronic health record,” two terms that HIPAA had never explicitly defined before.
Before, providers faced significant uncertainty about permitting health apps to access patient records because it was unclear whether patient data would be at risk once records were sent to an app that isn’t covered by HIPAA.
Now, the rule’s tightened language gives providers a clearer path to send health data to apps. It plainly states that if a patient asks for their records to be sent to a health app that meets the agency’s definitions, they must do so.
A personal health application, according to the final rule, is an app used by an individual to access their own health information, even if that information is drawn from multiple sources. The app must be controlled by that individual, rather than an organization or another person.
Commenters on the proposed rule were divided on whether the personal health app definition should be broader, covering more platforms and use cases, or narrower, to only include apps that met strict security and privacy standards. The HHS largely finalized the provision as proposed, without adding additional security limits, taking a broader approach.
An electronic health record, in the eyes of HIPAA, is now formally defined as an electronic record of “health-related information on an individual that is created, gathered, managed, and consulted by authorized health care clinicians and staff,” the rule states.
Among the rule’s many other elements is a provision that prohibits entities from imposing “unreasonable” identity verification requirements on an individual wanting to access their health records, such as requiring a patient to appear in person when there’s a method for remote verification available. Organizations must also start posting the cost of obtaining medical records on their websites.
Days before the rule was finalized, a coalition of healthcare executives wrote a letter to HHS asking it not to finalize the rule on the grounds that certain provisions would make it difficult for providers to confirm whether a third-party application has been authorized by a patient to receive their PHI. They also raised concerns about the move to loosen the verification requirements.
Despite the security concerns, the rule was finalized largely as proposed.
The HIPAA Security Rule, the privacy rule’s sister regulation that sets standards for the protection of electronic health information, is also due for a long-anticipated update next summer.